"Transparent proxy" is one of the most confusing terms in networking, because it names two different things. On a network, it is a proxy that your device never set up: the network redirects your traffic into it. On a proxy list, it is a grade: a proxy that hands your real address to every site you visit. This page explains both, from the standards that define them, and shows the second one in a small test we ran on our own machine.
The common name is also the one people use. Keyword Planner counts about 1,900 searches a month worldwide for "transparent proxy", against about 140 for "interception proxy", the name the standards prefer.
- transparent proxy
- interception proxy
What does "transparent proxy" mean on a network?
It means a proxy that the client did not choose. RFC 9110, the current HTTP standard, describes an "interception proxy" that is "also commonly known as a 'transparent proxy'". What sets it apart, the RFC says, is that it "is not chosen by the client". Instead, it "filters or redirects outgoing TCP port 80 packets (and occasionally other common port traffic)".
The same section says where these proxies live. They are "commonly found on public network access points", to make people sign up before they get online, "and within corporate firewalls to enforce network usage policies". Public Wi-Fi in hotels and airports, and office networks, are the usual places you meet one.
The idea is older than the web as most people know it. RFC 1919, from March 1996, describes how "the transparent proxy was born" from one complaint: ordinary proxies needed proxy-capable programs and trained users. A transparent proxy, it says, "appears like a packet filter to clients, and like a classical proxy to servers".
Why do the standards avoid the word?
Because "transparent" already meant something else in HTTP. In RFC 3040, from January 2001, a transparent proxy "does not modify the request or response beyond what is required for proxy authentication and identification". So the authors introduced a new name for the network kind, "interception proxy", for proxies "that receive redirected traffic flows from network elements performing traffic interception". They also recommended that the word transparent "is always prefixed to avoid confusion".
Squid, one of the most widely deployed proxy servers, adds a fourth use of the word. Its forwarded_for setting accepts a value named transparent, which means Squid "will not alter the X-Forwarded-For header in any way". With that many meanings in circulation, it pays to ask which one a page, a product or a colleague has in mind.
How does a network send your traffic through one?
The browser does nothing special. A router or firewall in the path catches the outgoing connection and hands it to the proxy. The browser still believes it is talking to the site. RFC 3040 puts it simply: interception proxies "require zero configuration of the user agent".
Squid's documentation for its http_port setting names the two ways it can receive such traffic:
intercept, "Support for IP-Layer NAT interception delivering traffic to this Squid port". The network rewrites the destination of the connection so that it lands on the proxy.tproxy, "Support Linux TPROXY (or BSD divert-to) with spoofing of outgoing connections using the client IP address". Here the proxy connects onward using your own address, so the site sees your IP and not the proxy's.
For both modes, the same documentation adds a short note: "disables authentication on the port". A browser that does not know about the proxy cannot answer a proxy's request for a password. That is why networks that need a login use a captive portal instead. RFC 6585 created status code 511, "Network Authentication Required", for this case. It is "intended for use by intercepting proxies that are interposed as a means of controlling access to the network".
What can an interception proxy see over HTTPS?
On a plain http connection, everything: the address, the headers and the content. HTTPS changes that. The browser runs its encrypted handshake with what it believes is the site, so a proxy in the path sees an encrypted stream. At the start of that handshake, the browser announces the name of the server it wants, a field defined in RFC 6066 as Server Name Indication. A network can pass or block a connection on that name without reading anything inside.
To read the content, the proxy has to decrypt it and sign a fresh certificate of its own, and the device must trust that certificate's authority. Company-managed computers often do, because IT installs the authority. On any other device the browser refuses the fake certificate, and you see a warning instead of the page. Our guide to ERR_CERT_AUTHORITY_INVALID covers that case.
What does "transparent" mean on a proxy list?
There, it is an anonymity grade, and it describes the headers a site receives. A transparent proxy passes your real address on, usually in X-Forwarded-For. An anonymous one hides your address but still marks the request as proxied, and an elite one adds nothing that names you or itself. Our page on transparent, anonymous and elite proxies covers the three grades in depth, with measurements from our free list.
Three headers do most of the work:
X-Forwarded-Forcarries the client's address. It is the header that makes a proxy transparent in this sense.Forwardedis its standard successor from RFC 7239. That RFC is blunt about anonymity: "when the purpose of using a proxy is to provide client anonymity, the proxy will not use the feature defined in this document".Viamarks the proxy itself. RFC 9110 requires a proxy to send it, so a proxy that leaves it out is bending the standard to stay quiet.
The two meanings meet in practice. Squid's documentation, for versions 5 to 7, lists both forwarded_for and via as on by default. So Squid appends the client's address and adds a Via header unless someone changes that. An office proxy on those defaults is transparent in both senses: your device never chose it, and it tells every site your internal address.
What does a site see through each kind?
We measured this on our own machine, with no real proxy, no real site and no traffic leaving the computer. A stub site on 127.0.0.1 answered every request with the address that connected to it and the proxy headers it received. In front of it, we ran two stub proxies: one that adds headers the way Squid does on its defaults, and one that adds nothing. The client sent its requests from a second loopback address, 127.0.0.2, so its own address would stand out.
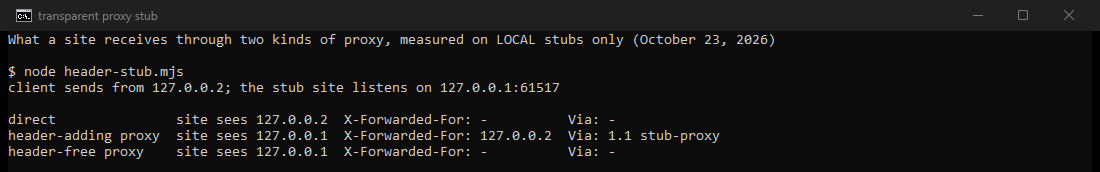
The result shows the whole difference in three lines. Without a proxy, the site saw the client's own address. Through the header-adding proxy, the connection came from the proxy's address, yet X-Forwarded-For still carried the client's 127.0.0.2, and Via announced the proxy. Through the header-free proxy, the site saw the proxy's address and nothing else. Changing the address is easy for any proxy. Only the headers decide whether the original address travels along.
How can you tell if you are behind a transparent proxy?
Check what a site actually receives. Your browser's developer tools will not show it, because they list the headers your browser sends, before any proxy in the path adds its own. You need a page that echoes back every header it received, loaded over plain http. Over https, a proxy your device does not trust cannot add headers at all.
- A
ViaorX-Forwarded-Foryou did not send means a proxy in the path added it. If the address inX-Forwarded-Foris your device's internal one, the proxy is transparent in both senses. - A login or terms page on a new network is a captive portal, which works through interception.
- On a network you run, the redirect rule sits in the router or firewall configuration, which is the authoritative place to look.
For a proxy you configure yourself, our proxy anonymity checker sends a request through it and reports whether it is elite, anonymous or transparent. To test a whole list at once, the online proxy checker takes up to 100,000 lines and reports each one's status, speed and anonymity.
Is a transparent proxy good or bad?
That depends on whose network it is and what you need. On a network you run, interception is a normal tool. It lets you cache, filter, apply a usage policy or require a login without touching a single device. That is what RFC 1919 promised in 1996. RFC 9110 is frank about the cost, though. Such intermediaries are "indistinguishable (at a protocol level) from an on-path attacker", and they often bring "security flaws or interoperability problems".
For privacy, a transparent proxy in the list sense hides nothing, because it passes your address to every site. If you choose a proxy to keep your address to yourself, check its grade first and pick an elite one. Our residential proxies cost $0.50/GB for one GB, falling to $0.44/GB at 2,000 GB+. You can grade any proxy, ours included, with the anonymity checker before you rely on it.
What we could not check
- We did not run an interception proxy on any network, and we tested nothing on our network or anyone's. The test above ran on local stubs, and its header-adding proxy imitates Squid's documented defaults; it does not run Squid.
- Squid's
forwarded_forandviapages list these defaults for versions 5 to 7 and say both directives are missing from version 8, which we did not examine. - Products that call their own features "transparent proxy" may use the word in yet another way. Read their documentation for what they mean.
- Standards and products change. This page is due for a check by January 23, 2027.
Sources
- RFC 9110: HTTP Semantics, June 2022, section 3.7 (interception proxies) and section 7.6.3 (Via), read October 23, 2026.
- RFC 3040: Internet Web Replication and Caching Taxonomy, January 2001: transparent, non-transparent and interception proxies.
- RFC 1919: Classical versus Transparent IP Proxies, March 1996.
- RFC 6585: Additional HTTP Status Codes, April 2012, section 6 (511 Network Authentication Required).
- RFC 7239: Forwarded HTTP Extension, June 2014.
- RFC 6066: TLS Extensions, January 2011, section 3 (Server Name Indication).
- Squid configuration reference: http_port, forwarded_for and via, read October 23, 2026.
- Google Keyword Planner, worldwide monthly searches, read October 23, 2026.