Free proxies for LinkedIn can open a public page, but they cannot make you anonymous there, and they cannot make scraping or extra accounts allowed. When our server opened the LinkedIn front page once on 28 September 2026, LinkedIn served its normal sign-in page. Our server sits in a datacenter, like many free proxies. What matters sits behind the sign-in. The LinkedIn User Agreement allows one account per person, in your real name, and forbids scrapers, bots and getting around its limits.
This page covers what LinkedIn answered our server and what its rules and Help Center say. It also shows how to view profiles without being seen, and what a free proxy puts at risk.
Do free proxies work for LinkedIn?
For a public page, maybe. For anything signed in, the rules decide. We sent LinkedIn two requests from our server, with no free proxy in between: one for its robots file and one for its front page. Both answered normally. The robots file opens with a notice: "The use of robots or other automated means to access LinkedIn without the express permission of LinkedIn is strictly prohibited". So we did not test sign-in or profiles through free proxies.
In our own pool on 28 September 2026 at 18:28 UTC, 1,319 of the 4,751 working free proxies on ordinary addresses were labelled datacenter. That is more than one in four. Counting every entry, 82.9 percent were. Either way, each one is an address shared by everyone who finds it.
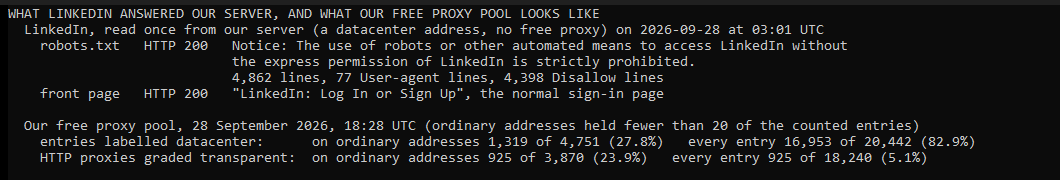
Some free proxies also pass your own address on. At the same time, 925 of the 3,870 working HTTP proxies on ordinary addresses were transparent, 23.9 percent, about one in four. Counting every entry, 5.1 percent were.
- Elite45%
- Anonymous31%
- Transparent24%
What LinkedIn allows
The User Agreement
The LinkedIn User Agreement, effective on 3 November 2025, never mentions proxies or VPNs. It rules on what you do, not on the address you come from. To use LinkedIn, "you will only have one LinkedIn account, which must be in your real name".
- One person, one account. No false identity, and no use of an account that belongs to someone else, "such as sharing log-in credentials or copying cookies".
- No scraping. No "software, devices, scripts, robots or any other means or processes (such as crawlers, browser plugins and add-ons or any other technology) to scrape or copy the Services".
- No bots. No "bots or other unauthorized automated methods" to add contacts, send messages or post.
- No getting around limits. No bypassing "any access controls or use limits of the Services (such as search results, profiles, or videos)".
LinkedIn "reserves the right to restrict, suspend, or terminate your account" when these rules are broken.
The Help Center
- Tools. LinkedIn does not permit third-party software, crawlers, bots, plug-ins or browser extensions that scrape, change or automate its website. Members who use them "risk having their accounts restricted or shut down."
- Restrictions. It names four kinds of reasons: content, profile, identity and automated tools violations.
- Getting back in. If a tool caused the restriction, LinkedIn asks you to disable it, and the account "will then automatically be re-enabled at the time specified on the suspension notification". To recover a restricted account, it can ask for a photo of a government ID through its verification provider.
None of the eight Help Center articles we read mentions proxies or VPNs.
How much LinkedIn catches
LinkedIn says that from July to December 2025, its automated defenses blocked 97.8 percent of the fake accounts it stopped. 99.7 percent were stopped before any member reported them. It counts over 1.3 billion members.
How to view a profile without being seen
A proxy changes the address your traffic comes from, not the account you are signed in with. Signed in, the view belongs to your account, whatever the proxy. LinkedIn has its own way to stay unseen: in private mode, the member sees you only as "LinkedIn Member". You switch it on in Settings & Privacy, under Visibility, at "Visibility when viewing other profiles". On a Basic (free) account, you then cannot see who viewed your own profile. Premium can.
Signed out, you see only the public profile the member allows. For a full profile, "visitors may need to log in to their LinkedIn accounts". A transparent proxy would also pass your own address on.
Your LinkedIn account is worth protecting
A LinkedIn account carries your real name, your work history and your contacts. A proxy is a server run by a stranger, in the middle of your traffic, and it adds no encryption of its own. LinkedIn serves its pages over HTTPS, so on a clean connection your password is encrypted in transit. A hostile proxy can still present a fake certificate and hope you click past the warning. In our tests of other websites on 27 September 2026, some free proxies presented certificates our client refused. A 2018 study of more than 107,000 listed open proxies found TLS man-in-the-middle attacks. LinkedIn writes that two-factor authentication "can greatly reduce unauthorized access to most accounts from new or unknown computers or devices". Never sign in through a free proxy. Our guide to whether free proxies are safe covers the rest.
Where a free proxy fits, and where it does not
| What you want to do | Free proxy? | Why |
|---|---|---|
| Open a public LinkedIn page | Maybe | Our server got the normal front page; we tested no free proxy on LinkedIn. |
| View a profile without being seen | No | Signed in, the view is yours. LinkedIn offers private mode. |
| Scrape profiles or jobs | No | The User Agreement forbids scrapers and bots. |
| Run more than one account | No | One account per person, in your real name. |
| Get around a restriction | No | LinkedIn asks you to disable the tool or verify your identity. |
| Get past a school, work or country block | No | That network sets its own rules, and this page gives no steps. |
| Log in | No | A hostile proxy can try to read your login. |
| Learn how a proxy works | Yes | A throwaway request, away from your accounts, costs nothing. |
Where a free proxy costs you
Anything you want to last is the wrong job for a free proxy. On ordinary addresses, more than one in four sits on a hosting network, and about one in four HTTP proxies passes your own address on. Those that worked and then stopped lasted a median 10 days, counting only addresses with fewer than 20 of them, without Amazon's networks or one June evening when our checker failed (measured 2026-09-28). For web tasks that have to keep running, such as checking your own site from another country, a residential proxy is the better tool. Its address belongs to a home connection, and it stays up while you work. Ours start at $0.44/GB, pay as you go, and purchased traffic has no scheduled expiry date. No proxy of any kind makes scraping or extra accounts allowed on LinkedIn.
Test any proxy before you use it
A free proxy that worked ten minutes ago may already be gone. Two things decide whether it is usable: whether it is alive, and where it actually exits. Paste any candidate into our free proxy checker, with no signup. It makes a real connection through the proxy and reports the exit address, country, latency and anonymity grade. From the command line, the same check is one request to our free checker API.
# Tests one proxy from our server: alive or dead, protocols, anonymity, latency, country
curl "https://hproxy.com/api/proxy-check?proxy=203.0.113.7:1080"
The anonymity grade matters here, since a transparent proxy passes your own address on. The full method is in how to check if a proxy is working.
The plain answer
Free proxies for LinkedIn are the wrong tool for anything that matters. LinkedIn served our server its normal front page. Its User Agreement still allows one account per person, and it forbids scrapers, bots and getting around its limits from any address. To view profiles without being seen, use the private mode LinkedIn offers. Never sign in through a free proxy. For web tasks that can fail, start with our free proxy list, and check anything you find elsewhere with the proxy checker.
How we measured
We opened https://www.linkedin.com/ and its robots file once each from our server in the United States on 28 September 2026 at 03:01 UTC, as a person would, and kept the answers as text. We ran no test of free proxies against LinkedIn. The datacenter labels and the transparent share come from one read-only query of our free proxy pool on 28 September at 18:28 UTC. Each figure leaves out addresses that held 20 or more of the entries it counts. The figure over every entry stands next to it. The refused certificates come from our tests of other websites on 27 September. We read the User Agreement, the Professional Community Policies, the Community Report and the Help Center articles below in a browser on 28 September 2026, in English. We store no proxy addresses from these tests, and every time is in UTC.
Sources
- LinkedIn, User Agreement, effective 3 November 2025, Professional Community Policies and robots file, read on 28 September 2026.
- LinkedIn Help, on prohibited software and extensions, automated activity, account restrictions, verifying your identity, private mode, who viewed your profile, public profile visibility and the sign-in security prompt, read on 28 September 2026.
- LinkedIn, Community Report, July to December 2025, read on 28 September 2026.
- Akshaya Mani, Tavish Vaidya, David Dworken and Micah Sherr, An Extensive Evaluation of the Internet's Open Proxies, arXiv 1806.10258, 27 June 2018.
- HProxy documentation: the proxy checker API, read 28 September 2026.