CentOS, Red Hat Enterprise Linux (RHEL), Rocky Linux and AlmaLinux keep a proxy setting in up to six places, and each one reaches a different set of programs. Give yum a proxy and RHEL's subscription-manager still cannot register; export one in the shell and sudo dnf upgrade still goes straight out. Pick the place that reaches the program you care about, then prove it with one command.
The four systems share their package tool, their sudo rules and their login files, so one page covers all of them, and it says where they differ. We did not install them for this page. Each command comes from the manual of the version a release ships, and where a manual and its program disagree, from the program's own source code: that is how we found that subscription-manager's manual page gives one of its options the wrong name. The sudo behaviour was measured on Fedora 44, which ships the same sudo rules and login chain, and CentOS 7's dead mirrors were measured from our workstation on 3 October 2026.
| Where you set it | What it reaches | What it leaves out |
|---|---|---|
| GNOME Settings, Network | Firefox on its default setting, Chromium, Chrome, GNOME's apps | Terminals, yum, dnf, sudo |
export in a terminal | curl, wget, yum and dnf started in that terminal | Other terminals, anything under sudo |
/etc/environment | The next login, and commands under sudo | Terminals already open |
/etc/yum.conf or /etc/dnf/dnf.conf | yum or dnf, for every repository | Everything that is not yum or dnf |
/etc/rhsm/rhsm.conf (RHEL only) | subscription-manager, and Red Hat's repositories in dnf | Other repositories, such as EPEL |
/etc/sudoers.d/ | Your exported names, carried into sudo | Users outside the wheel group |
Follow the desktop setting
Firefox
on its default, Use system proxy settings
Chromium and Chrome
read GNOME's setting when they run in GNOME
GNOME's own apps
the ones that use the network connection
Read their own setting
yum and dnf
proxy= in their config file, else https_proxy
subscription-manager
/etc/rhsm/rhsm.conf, else HTTPS_PROXY
curl and wget
http_proxy and https_proxy, in lower case
Anything run with sudo
starts with a short list of variables, no proxy
Which release uses which tool
The steps below depend on the package tool, and that changed after CentOS 7:
The package tool and its proxy file, by release
| Release | Package tool | Proxy file | One command |
|---|---|---|---|
| CentOS 7, RHEL 7 | yum 3 (3.4.3) | /etc/yum.conf | None: edit the file |
| RHEL, Rocky Linux and AlmaLinux 8 | dnf 4; the yum command runs it too | /etc/dnf/dnf.conf | dnf config-manager --save --setopt=proxy=... |
| RHEL, Rocky Linux and AlmaLinux 9 and 10, CentOS Stream 9 and 10 | dnf 4.14 (9) and 4.20 (10); yum is a link to it | /etc/dnf/dnf.conf; /etc/yum.conf is a link to it | dnf config-manager --save --setopt=proxy=... |
| RHEL only, every version | subscription-manager | /etc/rhsm/rhsm.conf | subscription-manager config --server.proxy_hostname=... |
| Fedora 41 and later, for comparison | dnf 5 | /etc/dnf/dnf.conf | dnf config-manager setopt proxy=... |
The CentOS 7 archive's packages; the dnf packages of CentOS Stream 9 and 10; yum.conf(5) of yum 3; rhsm.conf(5); a CentOS 8 dnf.log quoted on Server Fault (DNF version: 4.2.7); our Fedora 44 run
Fedora has its own guide; its dnf 5 writes some commands differently, and the difference matters in step 5.
What you need before you start
One proxy line, four parts
198.51.100.7Host:8080Port:hp_ir4k2Username:9fa2c1Password198.51.100.7:8080:hp_ir4k2:9fa2c1hp_ir4k2:9fa2c1@198.51.100.7:8080http://hp_ir4k2:9fa2c1@198.51.100.7:8080
GNOME takes the host and the port. yum, dnf and subscription-manager take all four, as separate options. Values shown are examples.
- A proxy address as
host:port, plus a user name and password if the proxy needs a login. If your provider sent the four values in another order, the proxy format guide sorts them out. - A terminal. Every step except the desktop one works on a server without a desktop.
- Root rights: an account in the
wheelgroup, which these systems let use sudo (%wheel ALL=(ALL) ALLin/etc/sudoers). - For a first test, any HTTP entry from our free proxy list will do. Free entries come and go, so test one first; the check further down shows how.
Step 1: the desktop (GNOME)
With a desktop installed, these systems run GNOME. Open Settings, choose Network, and open the proxy entry on that page. Set it to Manual and put the proxy's host and port under HTTP Proxy and HTTPS Proxy; newer GNOME versions also ask you to press Save. The same from a terminal, with GNOME's own keys, which work on every version:
gsettings set org.gnome.system.proxy mode 'manual'
gsettings set org.gnome.system.proxy.http host '198.51.100.7'
gsettings set org.gnome.system.proxy.http port 8080
gsettings set org.gnome.system.proxy.https host '198.51.100.7'
gsettings set org.gnome.system.proxy.https port 8080
Firefox follows this setting while its Connection Settings stay on Use system proxy settings, its default, and Chromium and Chrome read it when they run in GNOME. yum, dnf, subscription-manager and curl never do. The page has no field for a user name or password; Firefox asks for the login when it first connects. Our Fedora guide shows each GNOME and Firefox screen with numbers; RHEL's GNOME is older, so a label can differ.
Step 2: set the proxy for this terminal
export http_proxy="http://user:pass@host:port" https_proxy="http://user:pass@host:port" no_proxy="localhost,127.0.0.1,::1"
Both names start with http://, the one for HTTPS too: they name the proxy, and the proxy itself speaks plain HTTP. Write them in lower case. yum and dnf download through curl, and curl reads http_proxy only in lower case. A password with @ or : in it must be encoded in this address (%40, %3A); steps 4 and 5 show the options that take it as it is.
subscription-manager reads these names its own way: it looks for HTTPS_PROXY first, then https_proxy, HTTP_PROXY and http_proxy, and takes the first one it finds (from its code). The setting lives until you close the terminal. The Linux page has the details for curl, wget, git and pip.
Step 3: make it permanent
For yourself, add the export line to the end of ~/.bashrc. For every user, put the names into /etc/environment, one plain NAME=value line each:
http_proxy=http://user:pass@host:port
https_proxy=http://user:pass@host:port
no_proxy=localhost,127.0.0.1,::1
The file is read at login, so log out and back in. On these systems it also reaches commands you run with sudo. sudo's login file, /etc/pam.d/sudo, includes system-auth, and system-auth loads pam_env, the module that reads /etc/environment. We read that chain in the files of CentOS Stream 9 and 10 and in the profiles of authselect, the tool that writes system-auth on RHEL 8 and later, and measured the result on Fedora 44, which uses the same chain; step 7 shows it.
A script in /etc/profile.d/, which many guides suggest, exports the names in every login shell; like any exported name, sudo drops it. /etc/environment can be read by every user, so on a shared machine, keep a password out of it.
Step 4: yum on CentOS 7
CentOS 7 and RHEL 7 run yum 3, version 3.4.3 in CentOS 7's last release. It reads its proxy from /etc/yum.conf, under [main]:
[main]
proxy=http://host:port
proxy_username=user
proxy_password=pass
Three things from yum's manual and its code:
- The address needs its scheme. yum 3 accepts
http,https,ftp,socks4,socks4a,socks5andsocks5hin front. A line without one is refused withURL must be http, ftp, https, socks4, socks4a, socks5 or socks5h not "". - The login goes in as it is.
proxy_usernameandproxy_passwordtake the password unchanged, so an@in it needs no encoding there. proxy=libproxyasks the libproxy library for the proxy instead, so yum follows an automatic configuration.
For one command, --setopt sets the option for that run only:
sudo yum --setopt=proxy=http://host:port install wget
If yum then still fails with Could not resolve host: mirrorlist.centos.org, the proxy is not the problem. The next section is.
CentOS 7: the mirror errors no proxy can fix
CentOS Linux 7 reached its end of life on 30 June 2024, and its packages moved to an archive at vault.centos.org. Its repository files still point at mirrorlist.centos.org and mirror.centos.org. On 3 October 2026 we checked all three addresses from our workstation:
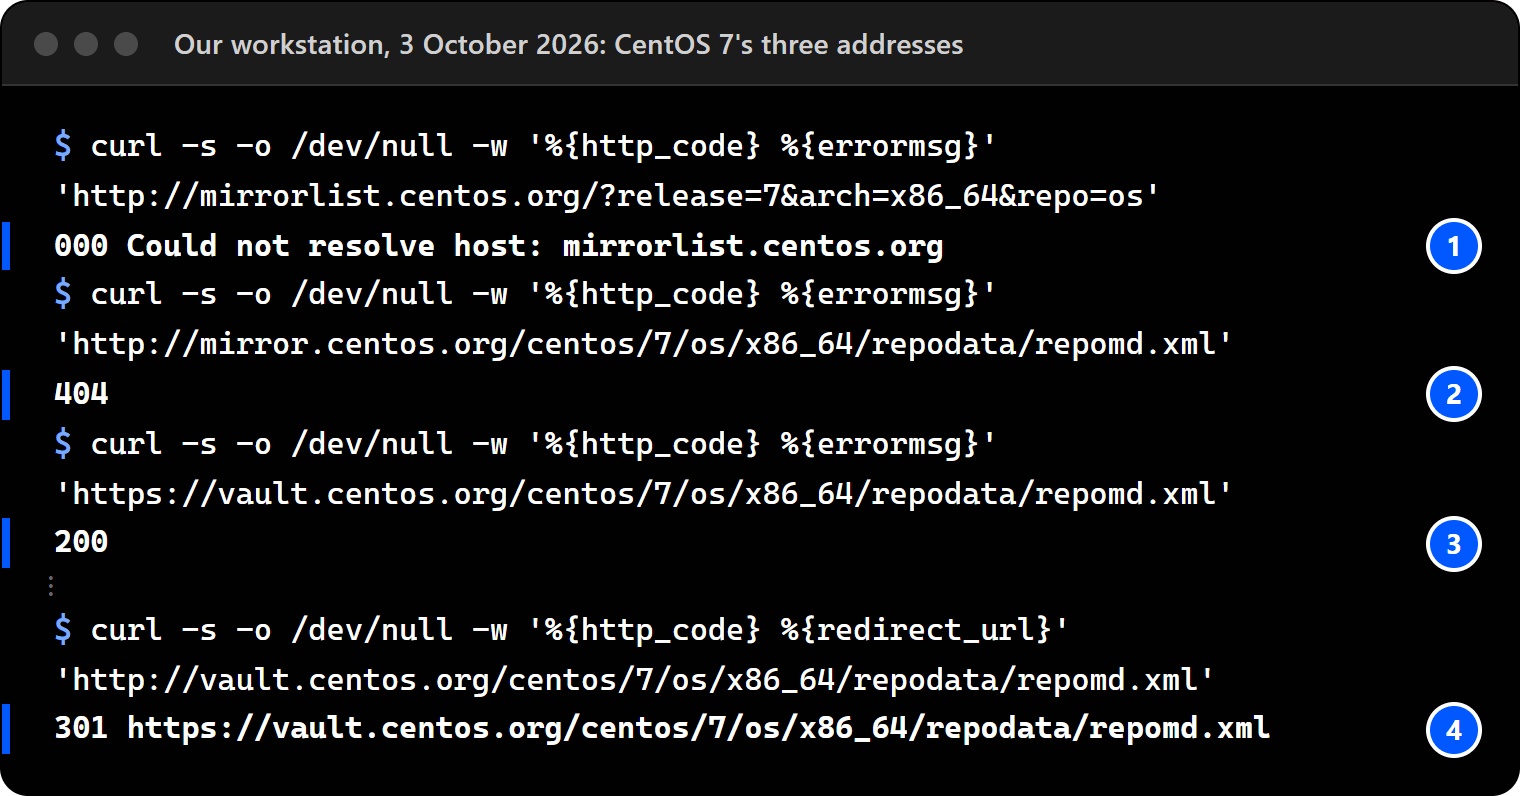
So this message, which a 2018 question on Server Fault has collected 574,453 views for, means that CentOS 7 is out of support, not that your proxy failed:
Could not retrieve mirrorlist http://mirrorlist.centos.org/?release=7&arch=x86_64&repo=os&infra=stock error was
14: curl#6 - "Could not resolve host: mirrorlist.centos.org; Unknown error"
The answers there point the CentOS repositories at the archive. This version changes only CentOS's own repository files and writes https://, which the archive redirects to anyway:
sudo sed -i -e 's/^mirrorlist=/#mirrorlist=/' -e 's|^#\?baseurl=http://mirror.centos.org|baseurl=https://vault.centos.org|' /etc/yum.repos.d/CentOS-*.repo
sudo yum clean all
sudo yum repolist
Behind a proxy, you need both fixes: the archive address, and the proxy from step 4. The archive receives no updates, so a CentOS 7 machine that must stay online belongs on a supported release. CentOS Linux 8 ended on 31 December 2021 and fails the same way, there as Failed to download metadata for repo 'AppStream'; its /var/log/dnf.log names mirrorlist.centos.org.
Step 5: dnf on RHEL, Rocky Linux and AlmaLinux 8 to 10
From release 8 on, the package tool is dnf 4, and the yum command runs it too. One command writes the proxy into /etc/dnf/dnf.conf:
sudo dnf config-manager --save --setopt=proxy=http://host:port
That is dnf 4's form. Fedora's dnf 5 writes it as dnf config-manager setopt proxy=..., and dnf 4 answers that form with one of the following arguments is required: --save --add-repo ..., a line from its config-manager code. If dnf answers No such command: config-manager instead, the package that brings the command, dnf-plugins-core, is missing, and installing it needs the proxy first. Then use the file, and install it afterwards with sudo dnf install dnf-plugins-core:
echo 'proxy=http://host:port' | sudo tee -a /etc/dnf/dnf.conf
A fresh /etc/dnf/dnf.conf on these systems holds [main] and five settings (gpgcheck=1, installonly_limit=3, clean_requirements_on_remove=True, best=True, skip_if_unavailable=False), so a line added at the end lands in the right section. On 9 and 10, /etc/yum.conf is a link to this same file, so guides that edit /etc/yum.conf are still right there.
To see what dnf will use:
dnf config-manager --dump | grep '^proxy'
dnf reads http_proxy and https_proxy from the environment only while its own proxy option is empty. Once the option is set, it wins.
A proxy with a user name and password
proxy=http://host:port
proxy_username=user
proxy_password=pass
The options take the password as it is, characters like @ included. dnf 4 hands them to librepo, the same download library dnf 5 uses, and on our Fedora test the @ worked there unchanged, while inside the proxy address it had to be %40.
If the proxy still answers 407 although the user name and password are right, name the method:
proxy_auth_method=basic
dnf's default, any, lets curl choose the method, and some proxies need it named. That line is the accepted fix in a CentOS 8 question on Unix & Linux with 15,494 views, where the login alone kept failing.
ls -l /etc/dnf/dnf.conf shows who can read the file: -rw-r--r-- means every user can read the password in it.
A proxy for one dnf command
sudo dnf --setopt=proxy=http://host:port install curl
One repository with its own proxy, or none
A repository's section in /etc/yum.repos.d/ can carry its own proxy=, which wins over the main one. config-manager writes it for you, with the repository's name in front:
sudo dnf config-manager --save --setopt=epel.proxy=http://host:port
To send one repository past the proxy, give it an empty proxy= (dnf 4) or proxy=_none_ (yum 3, and dnf 4 for compatibility) in that repository's section. The _none_ form is the accepted answer in a Super User question with 89,227 views. dnf's manual adds one detail: for that repository, the http_proxy and https_proxy variables count again, so a proxy left in the environment still applies.
Leave Red Hat's own repositories in redhat.repo alone. config-manager's manual warns that it can misbehave with repositories that subscription-manager generates, and subscription-manager rewrites that file anyway, as the next step shows.
Step 6: subscription-manager (RHEL only)
RHEL registers with Red Hat and downloads Red Hat's packages with certificates that subscription-manager manages, and subscription-manager has a proxy of its own. CentOS, Rocky Linux and AlmaLinux do not register with Red Hat, so they skip this step.
sudo subscription-manager config --server.proxy_hostname=host --server.proxy_port=port
sudo subscription-manager config --server.proxy_user=user --server.proxy_password=pass
Both commands write into the [server] section of /etc/rhsm/rhsm.conf. Three details decide whether it works:
- The host goes in without
http://. rhsm.conf's manual says the host should not contain the scheme. The program builds the address itself fromproxy_scheme(defaulthttp) and the host, so a host written withhttp://turns intohttp://http://...in the repository files. - The user name option is
proxy_user. subscription-manager's manual page, rhsm.conf(5), calls itproxy_username, but therhsm.confthat RHEL ships and the program's code both useproxy_user. Aproxy_usernameline is never read, and the proxy answers with a 407. - SELinux and ports other than 3128. rhsm.conf's manual warns that a proxy port other than 3128 may need an SELinux rule, depending on your policy:
sudo semanage port -a -t squid_port_t -p tcp 8080.sudo semanage port -l | grep squid_port_tlists the ports already allowed.
subscription-manager then writes the proxy into Red Hat's repositories too. Each time dnf runs on a registered RHEL machine, it prints Updating Subscription Management repositories. and rewrites /etc/yum.repos.d/redhat.repo, and every repository in that file gets proxy, proxy_username and proxy_password from rhsm.conf. A repository's own proxy wins over the one in dnf.conf, so for Red Hat's repositories, rhsm.conf decides:
/etc/rhsm/rhsm.conf
proxy_hostname, proxy_port, proxy_user, proxy_password
dnf starts
prints Updating Subscription Management repositories.
/etc/yum.repos.d/redhat.repo
proxy, proxy_username and proxy_password in every Red Hat repository
dnf downloads
Red Hat's repositories use rhsm.conf's proxy, the others dnf.conf's
In a Server Fault question about a 407 on RHEL 8, the asker found a proxy in every Red Hat repository file without knowing where it came from. This is where.
For one command, the proxy can also go on the command line:
sudo subscription-manager register --proxy=host:port --proxyuser=user --proxypassword=pass
subscription-manager looks up each value on its own: the command line first, then rhsm.conf, then the environment. So a forgotten HTTPS_PROXY can still supply a user name when rhsm.conf has none.
Step 7: carry exported names into sudo
sudo runs every command in a minimal environment. The /etc/sudoers of CentOS Stream 9 and 10, the source of RHEL 9 and 10, keeps display, language and terminal names and no proxy names, so a proxy you exported does not reach sudo dnf. Names from /etc/environment do, through the login chain from step 3:
- export in your shellhttp_proxy is set
- sudoenv_reset, no proxy names kept
- dnffinds no proxy, goes straight out
The default, without a proxy in dnf.conf
- /etc/environmentread at login
- sudosystem-auth loads pam_env again
- dnfuses the proxy
The login chain these systems ship
- export in your shellhttp_proxy is set
- sudoenv_keep for %wheel passes it on
- dnfuses the proxy
With the line in /etc/sudoers.d/proxy
We measured both of the first two rows on Fedora 44, whose sudo rules and login chain match:
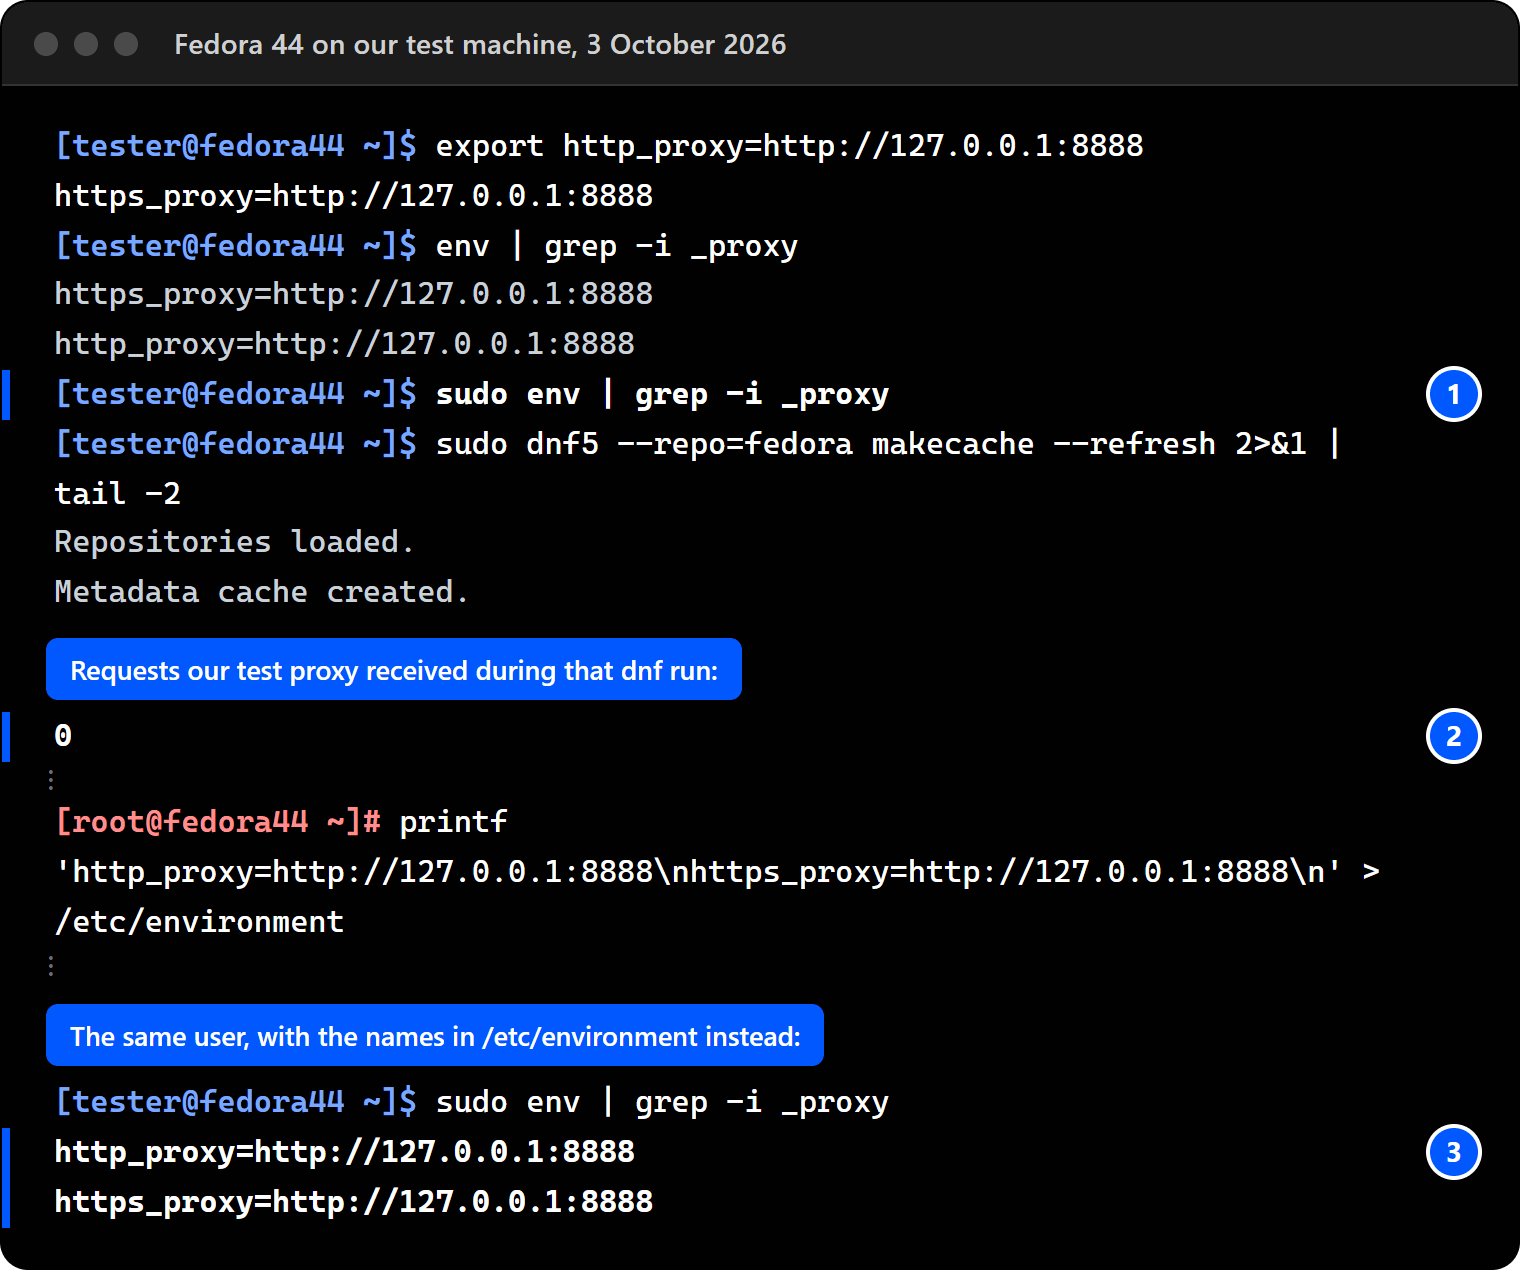
The option from step 4 or 5 is the cleaner fix for yum and dnf. For every command under sudo, add one line with visudo:
sudo visudo -f /etc/sudoers.d/proxy
Defaults:%wheel env_keep += "http_proxy https_proxy ftp_proxy all_proxy no_proxy"
The last line of /etc/sudoers, #includedir /etc/sudoers.d, looks like a comment, but the # belongs to the directive, the spelling sudo used before version 1.9.1; files in /etc/sudoers.d/ are read. For a single command, sudo -E keeps your whole environment. The wheel rule allows it, because a rule whose command is ALL implies the SETENV tag (sudoers manual).
A SOCKS5 proxy
yum and dnf both take a SOCKS5 proxy in the same option. Write socks5h://, so the proxy also resolves the host names:
proxy=socks5h://host:port
yum 3's code lists socks4, socks4a, socks5 and socks5h among its accepted schemes, and the top answer to "How to use SOCKS proxy with yum?" on Unix & Linux (43,375 views) uses exactly this line. dnf 4 passes the address to curl, which knows the same schemes; we ran the dnf 5 version of it on Fedora 44. subscription-manager's manual describes an HTTP proxy only.
Other programs
wget reads http_proxy and https_proxy, git has its own option, and Podman, the container tool these systems ship, pulls with the proxy variables of the command that starts it; we measured that on Fedora 44.
git config --global http.proxy http://user:pass@host:port
https_proxy=http://user:pass@host:port podman pull docker.io/library/alpine:latest
Check that it worked
curl -s https://www.cloudflare.com/cdn-cgi/trace | grep ^ip=
curl -s https://hproxy.com/api/ip/THE_ADDRESS_YOU_JUST_SAW
dnf config-manager --dump | grep '^proxy'
grep '^proxy' /etc/yum.repos.d/redhat.repo
sudo subscription-manager config --list | grep proxy
sudo env | grep -i _proxy
The first line prints the address a site sees; if it is the proxy's address, your traffic goes through the proxy. The second takes that address and returns its country, city, network and AS number. The next three show what dnf will use, what Red Hat's repositories carry and what subscription-manager has; on CentOS 7, read /etc/yum.conf instead, and skip the two RHEL lines elsewhere. The last shows what survives sudo. Then paste the entry into our free proxy checker, which reports status, protocol, anonymity, country and latency for every line. Free entries stop answering without notice; when a server has to keep updating, use a paid proxy instead.
When it does not work: the messages these systems print
The wording depends on the curl version a release ships: 7.29 on CentOS 7, 7.61 on 8, 7.76 on 9 and 8.12 on 10. The lines below come from real reports on Server Fault and from the programs' own code; the parts in angle brackets change with your setup.
yum on CentOS 7: the messages, what they mean, and the fix
| What you see | What it means | Fix |
|---|---|---|
Could not retrieve mirrorlist http://mirrorlist.centos.org/... error was 14: curl#6 - "Could not resolve host: mirrorlist.centos.org; Unknown error" | CentOS 7 has ended, and the name no longer exists. Not a proxy problem. | Point the repositories at vault.centos.org. |
[Errno 14] curl#7 - "Failed connect to <site>:<port>; Connection refused" | Nothing answered at the proxy. curl 7.29 names the site here, but the port is the proxy's. | Check proxy= in /etc/yum.conf. |
[Errno 14] curl#56 - "Received HTTP code 407 from proxy after CONNECT" | The proxy wants a login, and the one yum sent was missing or wrong. | Check proxy_username and proxy_password. |
URL must be http, ftp, https, socks4, socks4a, socks5 or socks5h not "" | The proxy line has no scheme in front. | Write proxy=http://host:port. |
Server Fault question 904304; yum 3's code; curl 7.29.0
dnf and subscription-manager on 8, 9 and 10: the messages, what they mean, and the fix
| What you see | What it means | Fix |
|---|---|---|
Curl error (56): Failure when receiving data from the peer for <url> [Received HTTP code 407 from proxy after CONNECT] | On 8 and 9: the proxy wants a login, and the one dnf sent was missing or wrong. On 10, curl 8.12 ends the line with [CONNECT tunnel failed, response 407]. | Check the login; if it is right, add proxy_auth_method=basic. |
Curl error (7): Couldn't connect to server for <url> [Failed to connect to <proxy> port <port>: Connection refused] | Nothing answers at the proxy address and port dnf uses. On 10 it reads Could not connect to server. | dnf config-manager --dump | grep ^proxy, then fix the address or start the proxy. |
Failed to download metadata for repo 'AppStream' | On CentOS Linux 8: the release ended on 31 December 2021, and dnf.log names mirrorlist.centos.org. | The archive, or a supported release. |
one of the following arguments is required: --save --add-repo ... | Fedora's dnf 5 syntax, given to dnf 4. | dnf config-manager --save --setopt=proxy=... |
No such command: config-manager. | The dnf-plugins-core package is missing. | Write the proxy into dnf.conf, then install the package. |
Proxy error: unable to connect to <proxy>:<port>: ... | From subscription-manager on RHEL: nothing answers at the proxy, or it refused the login. The text after the second colon says which. | sudo subscription-manager config --list | grep proxy |
Server Fault questions 1010136 and 1084027; dnf 4, dnf-plugins-core and subscription-manager code (1.28 to 1.30); curl 7.61.1, 7.76.1 and 8.12.1
Mistakes other guides make
These come up in guides and answers that rank for yum, dnf and RHEL proxy searches:
https://in front of an ordinary proxy. The proxy speaks plain HTTP. On our Debian and Fedora tests, apt and dnf hung for six minutes with it and then failed.- Fedora's commands on RHEL.
dnf config-manager setoptis dnf 5. RHEL, Rocky and AlmaLinux run dnf 4, which needs--save --setopt=. proxy_usernameinrhsm.conf. It is the manual page's name, and the program never reads it. Writeproxy_user.http://inproxy_hostname. subscription-manager adds the scheme itself.- Editing
redhat.repoby hand. subscription-manager rewrites it on the next dnf run. Changerhsm.confinstead. - Treating
mirrorlist.centos.orgerrors as proxy errors. On CentOS 7 and 8 they mean the release has ended.
Turning it off again
Each place is separate, and a forgotten one keeps sending traffic to a proxy that no longer exists:
- In open terminals, run
unset http_proxy https_proxy no_proxy, and remove your line from~/.bashrc. - Remove the lines from
/etc/environment, then log out and back in. - Delete the
proxy,proxy_usernameandproxy_passwordlines from/etc/yum.confor/etc/dnf/dnf.conf, and from any repository section that has its own. - On RHEL, remove the four values one by one:
sudo subscription-manager config --remove=server.proxy_hostname, then the same forserver.proxy_port,server.proxy_userandserver.proxy_password. The next dnf run removes them fromredhat.repoas well. - Run
sudo rm /etc/sudoers.d/proxy. - In GNOME, set the proxy back to off, or run
gsettings set org.gnome.system.proxy mode 'none'.
How we wrote this
We did not run CentOS, RHEL, Rocky Linux or AlmaLinux for this page. We read, for each tool, the version these releases ship: yum 3's manual and code, the CentOS 7 archive's package list (yum 3.4.3, curl 7.29.0), dnf 4's manual and the dnf packages of CentOS Stream 9 (dnf 4.14.0) and 10 (dnf 4.20.0), dnf-plugins-core's config-manager code, subscription-manager's manuals and its code (configuration, connection, repository writer, dnf plugin and error messages), the sudo package and PAM files of CentOS Stream 9 and 10, authselect's system-auth profiles, and curl's source at 7.29, 7.61, 7.76 and 8.12. Where a manual and its program disagreed, we followed the code.
Two things were measured. The sudo and /etc/environment behaviour comes from our Fedora 44 test machine on 3 October 2026, with a test proxy that logged every request; Fedora ships the same sudo rules and login chain. CentOS 7's mirrors and its archive were checked with curl from our workstation on 3 October 2026. The quoted error lines come from questions on Server Fault, Super User and Unix & Linux.
Limits: no command on this page was run on these four systems, and the error wording comes from code and from other people's reports, not from our own runs. The desktop steps are described, not shown on RHEL's GNOME.
Sources
All read on 3 October 2026.
- yum.conf(5) and the configuration code of yum 3: proxy, proxy_username, proxy_password, libproxy,
_none_and the accepted schemes (github.com/rpm-software-management/yum). - The dnf configuration reference, dnf 4: proxy, the curl variables, proxy_auth_method (dnf.readthedocs.io); the config-manager plugin and its code (dnf-plugins-core).
- The dnf packages of CentOS Stream 9 and 10: versions, the links for yum and yum.conf, the default dnf.conf (gitlab.com/redhat/centos-stream).
- Red Hat's RHEL 10 guide "Managing software with the DNF tool" (docs.redhat.com).
- rhsm.conf(5), subscription-manager(8) and subscription-manager's code: the proxy options, the repository writer and the error messages (github.com/candlepin/subscription-manager).
- The sudo packages of CentOS Stream 9 and 10: /etc/sudoers and /etc/pam.d/sudo; authselect's system-auth profiles (github.com/authselect).
- CentOS: end dates for CentOS Stream 8 and CentOS Linux 7, and the end of CentOS Linux 8 (blog.centos.org); the CentOS 7 archive (vault.centos.org).
- Rocky Linux and AlmaLinux on their compatibility with RHEL (rockylinux.org, almalinux.org).
- The curl man page, and curl's source at 7.29.0, 7.61.1, 7.76.1 and 8.12.1 (curl.se, github.com/curl).
- Questions on Server Fault (904304, 1010136, 1084027, 512561), Super User (393099) and Unix & Linux (43654, 592450).
- Our Fedora 44 test run of 3 October 2026, and our curl checks of CentOS 7's mirrors the same day.