pacman has no proxy setting. It downloads with curl, and curl takes its proxy from environment variables, so on Arch Linux, on Manjaro and in MSYS2 on Windows the whole job is to get the right variable to pacman, including through sudo. The right variable is not the one most guides set.
We did not install these systems for this page. Every statement comes from the source code of the versions shipped today: pacman 7.1, sudo 1.9.17, curl 8.22, Arch's login files and Manjaro's Pamac, plus one measurement from our workstation on 3 October 2026. Where we lean on a run, it is the Fedora 44 run behind our Fedora guide, which uses the same sudo and login chain as Arch, and the page says so.
| Where you set it | What it reaches | What it leaves out |
|---|---|---|
| The desktop's proxy setting (GNOME, KDE) | Browsers that follow the system setting | pacman, Pamac, terminals |
export in a terminal | pacman, curl and git started there without sudo | sudo pacman, other terminals, Pamac from the menu |
/etc/environment | Every login, sudo pacman, Pamac from the menu | Terminals already open |
/etc/sudoers.d/ | Your exported names, carried into sudo | Nothing else |
XferCommand in /etc/pacman.conf | pacman, through the downloader you name | Everything else |
Follow the desktop setting
Browsers
on their default, use the system setting
Read environment variables
pacman
through curl: https_proxy for every https mirror
Pamac (Manjaro)
the lower-case names of the process that starts it
pacman-mirrors (Manjaro)
Python's urllib: the proxy variables
Anything run with sudo
no exported names; /etc/environment's are kept
Why https_proxy is the variable that counts
curl picks the variable by the address it fetches: http_proxy for an http:// address, https_proxy (or HTTPS_PROXY) for an https:// one, and it never falls back from one to the other. So which kind of address pacman fetches decides everything. On 3 October 2026 we counted:
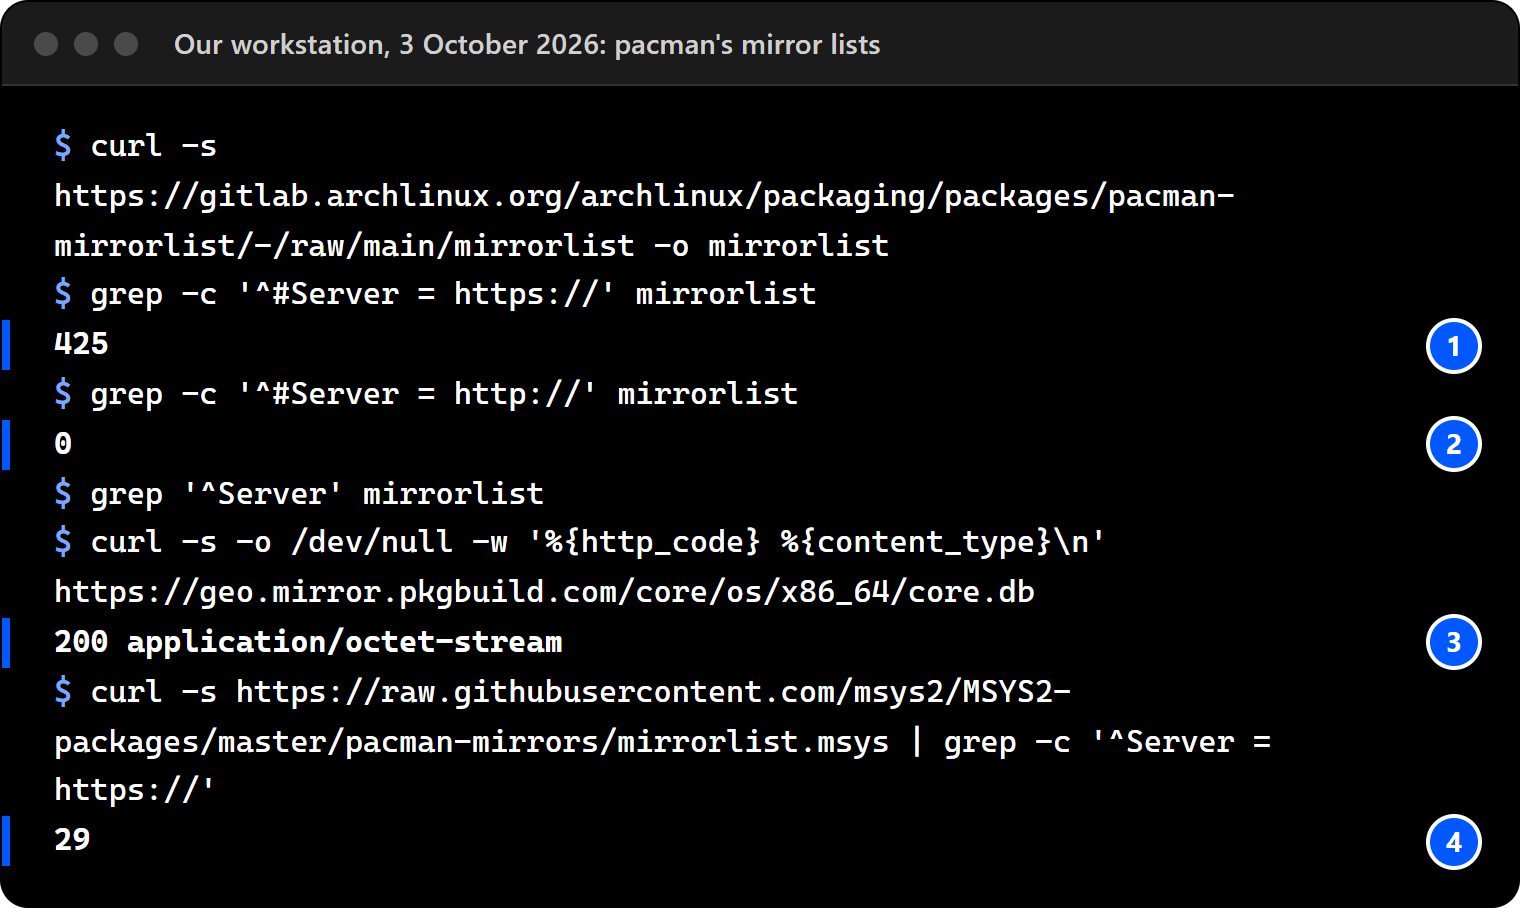
Arch builds that list with an https-only filter, so whichever mirrors you switch on, or reflector picks for you, are https. A guide that sets only http_proxy, as a 2008 answer on the Arch forums does, leaves pacman going straight out. Set both names, https_proxy first in importance.
What you need before you start
One proxy line, four parts
198.51.100.7Host:8080Port:hp_ir4k2Username:9fa2c1Password198.51.100.7:8080:hp_ir4k2:9fa2c1hp_ir4k2:9fa2c1@198.51.100.7:8080http://hp_ir4k2:9fa2c1@198.51.100.7:8080
pacman takes all four in one address, through the variables. Values shown are examples.
- A proxy address as
host:port, plus a user name and password if the proxy needs a login. If your provider sent the four values in another order, the proxy format guide sorts them out. - Root rights through sudo. Arch's default
/etc/sudoersships the line for thewheelgroup switched off; if your account cannot use sudo yet, enable that line withvisudoas root. - For a first test, any HTTP entry from our free proxy list will do. Free entries come and go, so test one first; the check further down shows how.
Step 1: set the variables for this terminal
export http_proxy="http://user:pass@host:port" https_proxy="http://user:pass@host:port" no_proxy="localhost,127.0.0.1,::1"
sudo -E pacman -Syu
Both names start with http://, the one for HTTPS too: they name the proxy, and the proxy itself speaks plain HTTP. Write them in lower case, because curl reads http_proxy only in lower case. Special characters in the login must be encoded: @ as %40, : as %3A.
sudo -E keeps your environment for that one command. It works because the wheel rule's command is ALL, which implies the SETENV tag (sudoers manual). Plain sudo pacman would drop the names, as step 3 explains.
Step 2: make it permanent with /etc/environment
Put the names into /etc/environment, one plain NAME=value line each, then log out and back in:
http_proxy=http://user:pass@host:port
https_proxy=http://user:pass@host:port
no_proxy=localhost,127.0.0.1,::1
On Arch this is the setting that reaches the most programs. Every login reads it, because pambase's system-login loads pam_env, and so does every sudo command: Arch's /etc/pam.d/sudo includes system-auth, which loads pam_env as well. So sudo pacman -Syu gets the proxy with no further step, and so does Pamac started from the menu on Manjaro. Fedora uses the same chain, and on our Fedora 44 test machine the names were present under sudo with and without a password prompt.
/etc/environment can be read by every user. On a shared computer, keep a password out of it and use step 3 instead.
Step 3: carry exported names into sudo
Arch installs sudo's own default /etc/sudoers, which keeps the names for visudo's editor and nothing about proxies, so an exported proxy is dropped by plain sudo:
- export in your shellhttps_proxy is set
- sudoenv_reset, no proxy names kept
- pacmangoes straight out
The default
- /etc/environmenttwo plain lines
- sudosystem-auth loads pam_env
- pacmanuses the proxy
Arch's sudo and login files
- export in your shellhttps_proxy is set
- sudoenv_keep passes it on
- pacmanuses the proxy
With the line in /etc/sudoers.d/proxy
To keep exported names for every sudo command, add one line with visudo:
sudo visudo -f /etc/sudoers.d/proxy
Defaults env_keep += "http_proxy https_proxy ftp_proxy all_proxy no_proxy"
The ArchWiki writes the same idea as Defaults env_keep += "*_proxy *_PROXY"; sudo accepts the * in env_keep.
pacman's own options
pacman reads no proxy, but four things in it matter behind one:
- The download sandbox. Arch's
/etc/pacman.confsetsDownloadUser = alpm, so pacman 7 downloads as the useralpm. Its sandbox code only switches the user and keeps the environment, so the proxy variables still apply. There is no need to switch the sandbox off for a proxy. - Timeouts. pacman stops a download that moves under 1 byte per second for 10 seconds, with curl's message
Operation too slow. When a proxy or a security gateway holds data back, add this under[options]; pacman's manual names it for exactly that case:
DisableDownloadTimeout
- An external downloader.
XferCommandhands every download to another program. pacman's manual offers it for "the more advanced proxy support that comes with utilities like wget"; with curl's variables, most proxies do not need it. - Signing keys.
pacman-keyfetches keys through gpg'sdirmngr, which ignores proxy variables unless told otherwise. The ArchWiki's fix is one line,honor-http-proxy, in/etc/pacman.d/gnupg/dirmngr.conf.
Manjaro: the same steps, plus Pamac
Manjaro builds on Arch's packages, so steps 1 to 3 apply unchanged. Two Manjaro tools add their own rules:
- Pamac, Manjaro's software manager, downloads in a daemon that runs as root. Pamac passes it five names from its own environment,
http_proxy,https_proxy,ftp_proxy,socks_proxyandno_proxy, all in lower case. Started from the menu, Pamac has the environment of your login, so names from/etc/environmentarrive. Exports in~/.bashrcdo not, and neither does the proxy you set in the desktop's network settings, which Pamac never reads. - pacman-mirrors, the tool behind
sudo pacman-mirrors --fasttrack, fetches with Python'surllib, which reads the proxy variables. Run with sudo, it needs them from/etc/environmentor step 3, like pacman.
MSYS2 on Windows
MSYS2 ships pacman too, version 6.1, built on curl, so the same rule holds: all 29 of its mirrors are https, and https_proxy or HTTPS_PROXY decides. MSYS2's own documentation has no page about proxies. Two ways to set it:
export https_proxy="http://user:pass@host:port" http_proxy="http://user:pass@host:port"
pacman -Syu
Or once for Windows, in cmd, followed by a new MSYS2 window, which starts with Windows' variables:
setx HTTPS_PROXY http://user:pass@host:port
curl reads HTTPS_PROXY in upper or lower case, so the Windows-style name works for MSYS2's https mirrors.
Many company proxies also open HTTPS traffic and re-sign it with their own certificate. MSYS2 then fails with SSL certificate problem: self-signed certificate in certificate chain (OpenSSL before 3.0 wrote "self signed"), followed by too many errors from mirror.msys2.org. The accepted answer on Stack Overflow, with 60 votes on a question viewed 41,666 times, is to export the company's certificate, copy it to C:\msys64\etc\pki\ca-trust\source\anchors\, and run update-ca-trust in the MSYS2 shell. A later answer there explains why: MSYS2's OpenSSL does not read the Windows certificate store. On Arch itself, the ArchWiki's command for the same job is sudo trust anchor certificate.crt.
Check that it worked
env | grep -i _proxy
sudo env | grep -i _proxy
curl -s https://www.cloudflare.com/cdn-cgi/trace | grep ^ip=
curl -s https://hproxy.com/api/ip/THE_ADDRESS_YOU_JUST_SAW
sudo pacman -Sy
The first two show which names you have and which survive sudo; https_proxy must be in both. The third prints the address a site sees; if it is the proxy's address, your traffic goes through the proxy. The fourth takes that address and returns its country, city, network and AS number. The last refreshes pacman's databases through the proxy. Then paste the entry into our free proxy checker, which reports status, protocol, anonymity, country and latency for every line. Free entries stop answering without notice; for daily work, use a paid proxy instead.
When it does not work: pacman's messages
pacman prints failed retrieving file '<file>' from <mirror> : followed by curl's reason. The reasons below are curl 8.22's wording, the version Arch ships; another curl version may word some of them differently.
pacman's messages behind a proxy, what they mean, and the fix
| What you see after the colon | What it means | Fix |
|---|---|---|
Failed to connect to <mirror>:443 over proxy <proxy> after <N> ms: Could not connect to server | Nothing answers at the proxy address and port pacman uses. | Check env | grep -i _proxy; fix the address or start the proxy. |
CONNECT tunnel failed, response 407 | The proxy wants a login and did not get the right one. | Put user:pass@ into the variable; encode @ as %40. |
Operation too slow. Less than 1 bytes/sec transferred the last 10 seconds | The proxy or a gateway held the data back for 10 seconds. | Add DisableDownloadTimeout under [options]. |
SSL certificate problem: self-signed certificate in certificate chain | A proxy re-signs HTTPS with a certificate the system does not trust. | Arch: sudo trust anchor <file>; MSYS2: the anchors folder and update-ca-trust. |
warning: too many errors from <mirror>, skipping for the remainder of this transaction | pacman gave up on that mirror after repeated failures. | Fix the reason printed above it. |
error: failed to synchronize all databases (...) | The summary after the lines above. | Read the failed retrieving file lines first. |
pacman 7.1.0 and curl 8.22.0 source; Stack Overflow question 69348953 (MSYS2)
Mistakes other guides make
These come up in the pages and answers that rank for pacman proxy searches:
- Only
http_proxy, orhttp_proxyandftp_proxy. Arch's and MSYS2's mirrors are all https; curl never readshttp_proxyfor them. ~/.bashrconly. It reaches the terminal, notsudo pacmanand not Pamac started from the menu.- wget as
XferCommandto get proxy support. That advice is from 2009; pacman's own curl reads the variables. - Switching the download sandbox off. It keeps the proxy variables, so it is not the cause.
Turning it off again
- In open terminals, run
unset http_proxy https_proxy no_proxy, and remove your line from~/.bashrc. - Remove the lines from
/etc/environment, then log out and back in. - Run
sudo rm /etc/sudoers.d/proxyif you made it. - Remove
DisableDownloadTimeoutor anXferCommandline from/etc/pacman.confif you added one. - In MSYS2, close the shell; for a Windows variable, run
setx HTTPS_PROXY ""incmdand delete it under Environment Variables.
How we wrote this
We did not run Arch Linux, Manjaro or MSYS2 for this page. We read the source of pacman 7.1.0 (its downloader, its sandbox, its manual) and Arch's shipped /etc/pacman.conf, sudo 1.9.17p2's default sudoers, Arch's /etc/pam.d/sudo and pambase's system-auth and system-login, curl 8.22.0, the pacman-mirrorlist package, Manjaro's libpamac and pacman-mirrors, and MSYS2's pacman package, mirror list and documentation. The package versions come from archlinux.org on 3 October 2026.
One measurement ran on our workstation that day: the mirror lists above, fetched with curl. The sudo behaviour rests on our Fedora 44 run, which uses the same PAM chain. Real problems and answers come from the ArchWiki, the Arch Linux and EndeavourOS forums, Unix & Linux and Stack Overflow.
Limits: no command on this page ran on Arch, Manjaro or MSYS2 itself. Manjaro's own pacman.conf and sudoers were not read, because its source server did not answer; Pamac was read from its GitHub mirror. The proxy dialogs of KDE and GNOME are not covered.
Sources
All read on 3 October 2026.
- Arch Linux packages: pacman 7.1.0, sudo 1.9.17p2, pambase 20260616, curl 8.22.0, pacman-mirrorlist 20260610 (archlinux.org).
- pacman 7.1.0:
lib/libalpm/dload.c,lib/libalpm/sandbox.c, pacman.conf(5); Arch's packaging of pacman, sudo, pambase and pacman-mirrorlist (gitlab.archlinux.org). - sudo 1.9.17p2: the default sudoers,
plugins/sudoers/sudoers.in(github.com/sudo-project). - curl 8.22.0 source and the curl man page (github.com/curl, curl.se).
- libpamac and pacman-mirrors (github.com/manjaro).
- MSYS2-packages: pacman 6.1.0 and its mirror lists; MSYS2's documentation (github.com/msys2).
- ArchWiki: Proxy server, Pacman (troubleshooting), Transport Layer Security (wiki.archlinux.org).
- Arch Linux Forums threads 67885 and 52132; EndeavourOS Forum, "How to set proxy for pacman?"; Unix & Linux questions 218376, 649771 and 270503; Stack Overflow questions 69348953 and 47328474.
- Our curl measurement of the mirror lists, 3 October 2026, and our Fedora 44 run of the same day.