You cannot fake the IP address a website sees on a normal connection. The site replies to the address the connection came from, so a made-up address never receives the reply and the page never loads. What people call a fake IP is one of four things. Two are forgeries: a packet that cannot load a page, and a header that fools only careless servers. The third is the real address of another machine, such as a proxy. The fourth is a reserved address, safe to use in examples.
We tested the header trick on 10 October 2026 with small stub servers on one machine. The rest of this page rests on the internet standards that decide how addresses work.
The four things called a fake IP
| What people mean | What it does | Good for |
|---|---|---|
| A spoofed packet (forged source address) | The reply goes to the forged address, so no connection opens | Nothing a reader of this page needs |
A forged header such as X-Forwarded-For | Fools only a server that believes the header | Testing your own server's settings |
| Another machine's real address (proxy, VPN, Tor) | The site sees that machine's address, which is real | Privacy, regional versions of sites, scraping |
A reserved address (192.0.2.1, 10.0.0.5) | Points at nobody on the public internet | Examples, test data, forms in documentation |
Why a spoofed address cannot load a page
Opening a web page starts with a TCP connection. The TCP standard calls the start a "three-way handshake". One side sends a request to connect, the other side answers, and the first side confirms. The answer goes to the source address on the request. If that address is forged, the answer goes to someone else, and the connection never opens.
So spoofing is a one-way trick. It can push packets out, and it has been used in attacks for exactly that reason. Network providers are told to stop it at the edge. RFC 2827, published as best current practice in May 2000, describes ingress filtering "to prohibit DoS attacks which use forged IP addresses". Neither the handshake nor the filter leaves room for a spoofed address that browses.
Can a header fake your IP?
Only for a server that chooses to believe it. Proxies and load balancers add a header such as X-Forwarded-For or Forwarded to tell the server who the original client was. The standard for Forwarded warns that the header "cannot be relied upon to be correct". Every node on the way to the server may change it, "including the client making the request".
We built three stubs on one machine to see what that means in practice. A naive server believed the first X-Forwarded-For value. A strict server used the address of the TCP connection. A transparent proxy added the client's address to the header, as such proxies do.
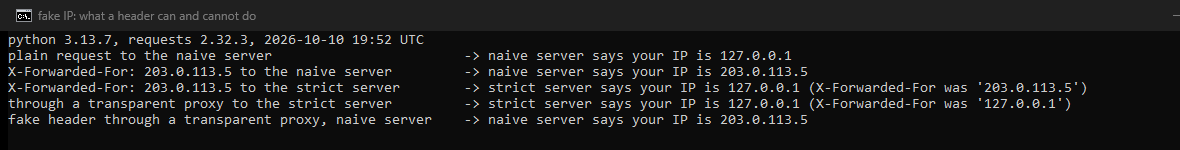
| Request | What the server reported |
|---|---|
| Plain request, naive server | 127.0.0.1, the real address |
X-Forwarded-For: 203.0.113.5, naive server | 203.0.113.5, the fake one |
X-Forwarded-For: 203.0.113.5, strict server | 127.0.0.1, and it showed the header it ignored |
| Through a transparent proxy, strict server | 127.0.0.1, with the client's address in X-Forwarded-For |
| Fake header through the transparent proxy, naive server | 203.0.113.5, because it read the first value |
Two lessons follow. A forged header changes nothing for a site that reads the connection. And a transparent proxy hands your real address to the site in that same header. That is the opposite of what most people want from a proxy.
The fake IP that works: another real address
When a site sees a different address, it is because your traffic went through another machine and the site talked to that machine. The address is real; it is just not yours. A proxy, a VPN and Tor all work this way. The TCP handshake works because the replies go to that machine, which passes them back to you.
The catch is the one our test showed. A proxy can still pass your address on in a header. Our free proxy checker reports a proxy's anonymity grade, which says whether it does. Our guide to how websites detect proxies covers the other signals a site uses.
Fake IP addresses for examples and tests
Some addresses look real and point at nobody. The standards set them aside:
- For documentation and examples: RFC 5737 reserves
192.0.2.0/24,198.51.100.0/24and203.0.113.0/24. They "are provided for use in documentation" and "SHOULD NOT appear on the public Internet". - For private networks: RFC 1918 reserves
10.0.0.0/8,172.16.0.0/12and192.168.0.0/16for private internets.
A lookup has nothing to say about these addresses. Our IP lookup rejects private, loopback, CGNAT and other reserved ranges with 400 private_ip, because they have no public location.
What a fake IP generator gives you
A generator prints addresses that look random. It does not touch the address your connection uses, so it hides nothing. A random address can also belong to a real network, which makes it a poor choice for test data or a form example. Take one from the documentation blocks above instead.
For a different address that a site will accept, use a real one: a proxy. Check its anonymity grade first, or use our residential proxies. A line from them carries your traffic from an address that is not yours.
What this page could not check
We tested headers against stub servers on one machine, not against real sites. We did not measure how many real sites trust forwarding headers. We did not send spoofed packets. That needs raw network access and is the method used in attacks, so the page relies on the TCP and ingress filtering standards instead. We did not test VPNs or Tor. Standards change slowly, but we will reread the ones cited and run the header test again by 10 April 2027.
Sources
- RFC 9293, Transmission Control Protocol (TCP), IETF, August 2022: section 3.5, the three-way handshake.
- RFC 2827 (BCP 38), Network Ingress Filtering, IETF, May 2000.
- RFC 7239, Forwarded HTTP Extension, IETF, June 2014: section 8, Security Considerations.
- RFC 5737, IPv4 Address Blocks Reserved for Documentation, IETF, January 2010.
- RFC 1918 (IETF, February 1996), Address Allocation for Private Internets: the three private blocks.
- HProxy documentation: IP location and ASN API, and the free proxy checker API, read 10 October 2026.
- Our own test on 10 October 2026: headers_test.py with Python 3.13.7 and requests 2.32.3.