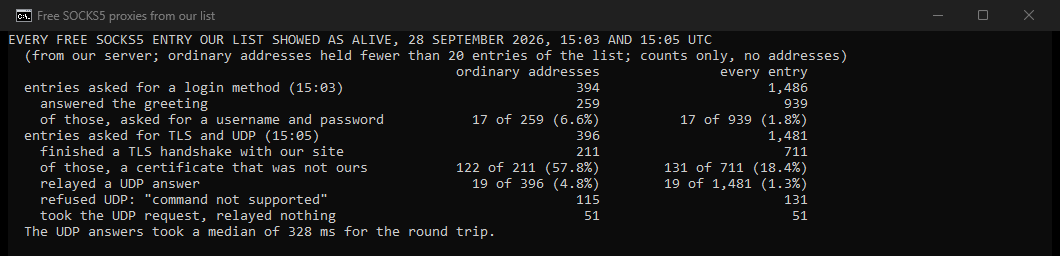
A free SOCKS5 proxy almost never needs a password, rarely carries UDP, and does nothing to protect what you send through it. We checked that on 28 September 2026 at 15:03 UTC, on every free SOCKS5 entry our list showed as alive. On addresses that held fewer than 20 entries of the list, 17 of the 259 that answered asked for a username and password. 19 of 396 relayed a UDP answer. And 122 of the 211 that finished a TLS handshake with our site handed back a certificate that was not ours.
This page answers what a list cannot: logins, UDP, and what a free SOCKS5 proxy does to your traffic. For the entries themselves, use the SOCKS5 view of our free proxy list. For how SOCKS5 differs from SOCKS4, see SOCKS4 vs SOCKS5.
What we asked every free SOCKS5 proxy
SOCKS5 is defined in RFC 1928. A client opens a connection and first offers the login methods it knows, and the proxy picks one. Then the client asks for a TCP tunnel with CONNECT, or for a UDP relay with UDP ASSOCIATE. We asked each entry three things. Which login did it want? Would it open a tunnel to our own site for a TLS handshake? And would it relay one UDP packet to a public DNS resolver?
Each figure leaves out addresses that held 20 or more entries of the list, and where that moves a figure a lot, the page gives both.
Username and password
RFC 1928 lists the methods a proxy can pick, among them "X'00' NO AUTHENTICATION REQUIRED", "X'02' USERNAME/PASSWORD" and "X'FF' NO ACCEPTABLE METHODS". We offered the first two to every entry.
- Most need none. On ordinary addresses, 242 of the 259 entries that answered the greeting needed no login. 17 asked for a username and password, 6.6 percent. Counting every entry, 17 of 939 asked.
- A proxy that asks for a password is closed to you. A free list gives an address and a port. A proxy that asks for a login belongs to someone who did not share it, so there is no free way in.
- A SOCKS5 password is not a secret on the wire. RFC 1929, which defines the method, warns that "the request carries the password in cleartext". It advises against the method where "sniffing" is possible.
- Browsers cannot send one anyway. The Chromium documentation says "No authentication methods are supported for SOCKSv5 in Chrome".
UDP
SOCKS5 can relay UDP. In RFC 1928, UDP ASSOCIATE sets up "an association within the UDP relay process to handle UDP datagrams." Games, calls and DNS lookups use UDP, so this is the mode people look for. It is also the one free proxies skip.
- 19 of 396 relayed a UDP answer on ordinary addresses, 4.8 percent, at a median of 328 milliseconds for the round trip. Counting every entry, 19 of 1,481.
- 115 refused the command outright with RFC 1928 reply 7, "Command not supported". Another 51 accepted the request and relayed nothing.
- Chrome would not use it. The Chromium documentation says SOCKS5 in Chrome "cannot be used to relay UDP traffic".
What a free SOCKS5 proxy does to your traffic
SOCKS5 forwards bytes. It adds no encryption of its own. RFC 1928 says the security "is highly dependent on the particular authentication and encapsulation methods" the two sides agree on, and a free proxy that asks for no login agrees on none.
- HTTPS is your protection, if you check it. Through a SOCKS5 tunnel, your client runs TLS straight to the site. On ordinary addresses, 122 of the 211 entries that finished a TLS handshake with our site handed back a certificate that was not ours. It was an expired one, from an issuer named "None, LLC". Counting every entry, 131 of 711. A client that checks certificates stops there. One that does not would have sent its traffic to the proxy.
- Plain HTTP is readable. Anything sent without TLS passes through the proxy as it is.
- Name lookups can leak. The curl manual describes
--socks5-hostnameas "Use the specified SOCKS5 proxy (and let the proxy resolve the hostname)", and--socks5as "Use the specified SOCKS5 proxy - but resolve the hostname locally". The requests library says the same ofsocks5handsocks5. With the local form, your own resolver sees every site you visit.
The rest of the safety picture, with more tests, is in are free proxies safe.
Using a free SOCKS5 proxy
# socks5h: the proxy looks up the name; curl checks the certificate by default
curl -x socks5h://203.0.113.7:1080 --max-time 20 https://httpbin.org/ip
- Take entries that need no login. Our free proxy list API returns the entries alive on their last check with
protocol=socks5, with no key and no signup. - Keep certificate checks on. The curl manual says every secure connection "is verified to be secure before the transfer takes place." Never pass
-kto curl, or its equivalent in any tool, through a free proxy. - Test right before you use it. Our free proxy checker reports whether an entry is alive and what it speaks, and SOCKS5 proxy errors explained covers what each failure means.
- Keep it to public pages. Never sign in, pay or type personal details through a free proxy.
When free is not enough
For a SOCKS5 connection that has to keep working, with a login that is yours, a residential proxy is the better tool. Our residential lines answer SOCKS5 with the same username and password as HTTP, and our SOCKS5 residential proxies page covers the UDP relay that comes with Premium. Ours start at $0.44/GB, pay as you go, and purchased traffic has no scheduled expiry date.
The plain answer
Free SOCKS5 proxies rarely need a password: 17 of 259 on ordinary addresses asked for one. They rarely carry UDP: 19 of 396 relayed an answer. And more than half of those that finished a TLS handshake with our site, 122 of 211, handed back a certificate that was not ours. Use socks5h, keep certificate checks on, and never send anything private through one.
How we measured
On 28 September 2026, two scripts on our server in the United States took every entry our free list API showed as alive with the socks5 flag. At 15:03 UTC, the first sent each of 1,486 entries one SOCKS5 greeting that offered no login and a username and password, and recorded the method each chose. At 15:05 UTC, the second asked each of 1,481 entries for a CONNECT tunnel to our own site with a TLS handshake. It compared the certificate with the one our server gets directly, and asked for a UDP relay of one DNS question to the public resolver 1.1.1.1. Each figure leaves out addresses that held 20 or more entries of the list, and gives the every-entry figure where the two differ a lot. We sent no other traffic through any proxy, we store no proxy addresses, and every time is in UTC.
Sources
- IETF, RFC 1928: SOCKS Protocol Version 5, March 1996.
- IETF, RFC 1929: Username/Password Authentication for SOCKS V5, March 1996.
- The curl manual: curl.1, on
--socks5and--socks5-hostname, read 28 September 2026. - The requests documentation: Advanced Usage, on SOCKS, read 28 September 2026.
- Chromium documentation: Proxy support in Chrome, read 28 September 2026.
- HProxy documentation: the free proxy list API, read 28 September 2026.